Tina Butler · 11 October 2026
Reimagining Security Audits: The Impact of KnoxOpen on Startup Compliance Processes
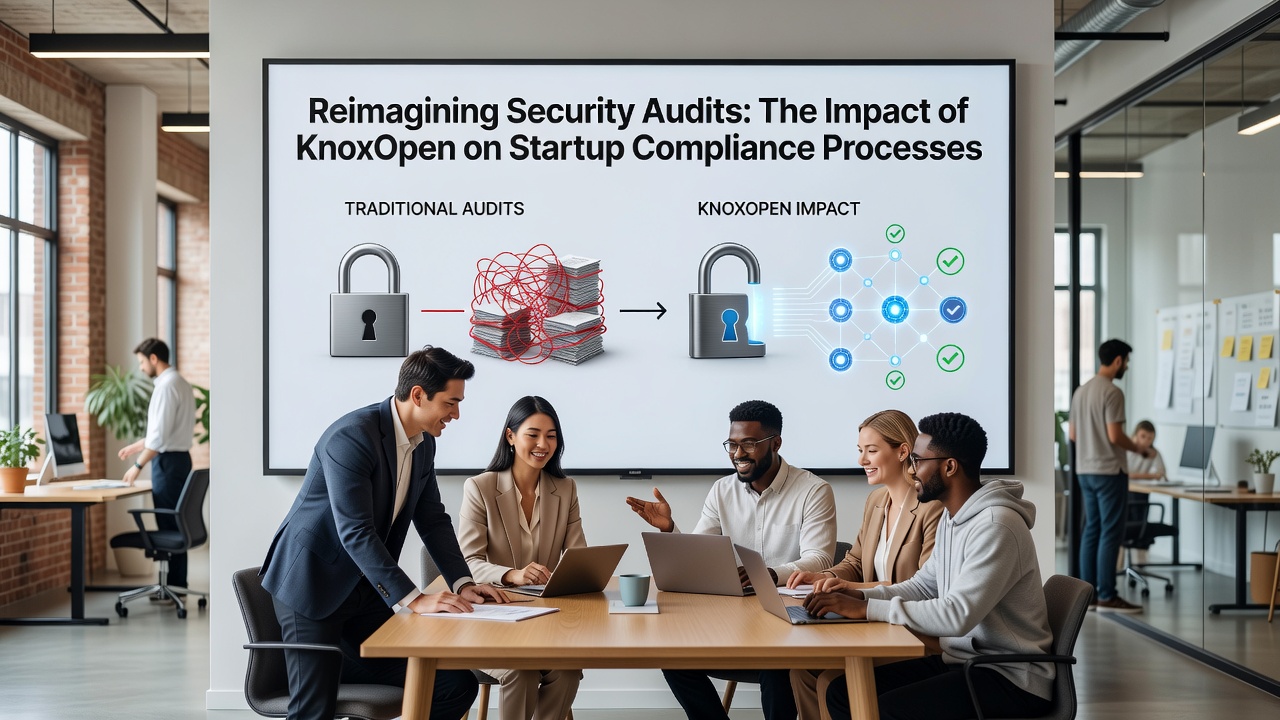
Security audits have long presented startups with layered requirements that span documentation, vulnerability scanning, and regulatory alignment, yet KnoxOpen has introduced an open framework that consolidates these steps into a single platform. Researchers at multiple institutions have tracked how this tool automates evidence collection and maps controls directly to standards such as ISO 27001 and NIST frameworks, which reduces the manual effort traditionally required during preparation phases. Observers note that the platform’s modular design allows teams to plug in existing code repositories and cloud environments without extensive reconfiguration.
Traditional Audit Challenges for Early-Stage Companies
Many startups operate with limited security personnel while still needing to demonstrate compliance to investors and enterprise customers, and data from industry reports indicate that audit cycles often stretch across several months when performed manually. KnoxOpen addresses these constraints by delivering continuous monitoring features that flag deviations in real time, which enables founders to address issues before formal assessments begin. Those who have implemented the system report that integration typically occurs within weeks rather than quarters because the codebase remains publicly inspectable and extensible through community contributions.
Core Capabilities Driving Efficiency Gains
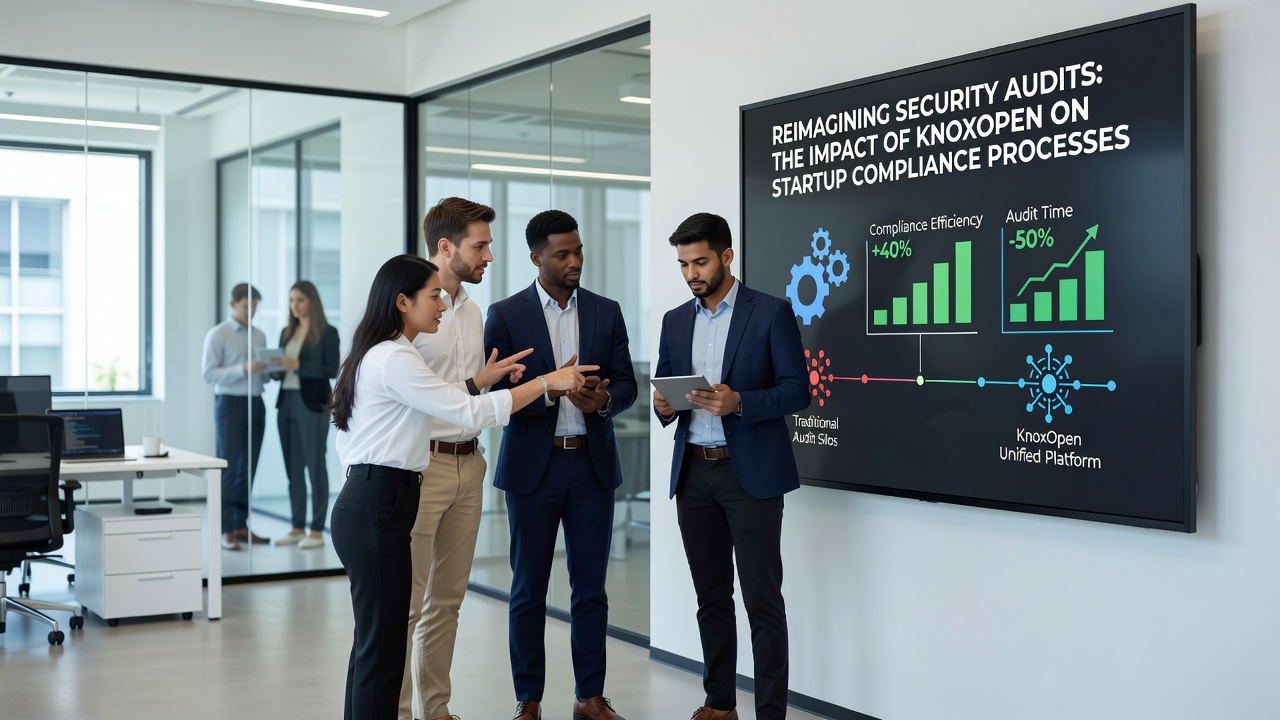
KnoxOpen combines policy-as-code templates with automated evidence gathering that pulls logs from common infrastructure providers, and this approach aligns controls across multiple jurisdictions simultaneously. In October 2026, updates to the platform incorporated new modules for emerging data residency rules in the Asia-Pacific region, which further expanded its utility for globally distributed teams. Studies from academic groups show that organizations using similar open tools cut audit preparation time by measurable percentages when compared with legacy spreadsheet-based methods.
Real-World Adoption Patterns Among Startups
One early-stage fintech company integrated KnoxOpen during a Series A funding round and completed its SOC 2 Type I audit in under six weeks, whereas previous attempts had required external consultants for comparable results. Another case involved a health-tech venture that leveraged the platform’s open API to connect its internal ticketing system directly to compliance dashboards, which eliminated duplicate data entry and allowed engineering leads to track remediation progress without separate reporting tools. These examples illustrate how the technology shifts responsibility toward product teams rather than isolating compliance as a separate function.
Integration With Regulatory and Standards Bodies
KnoxOpen maintains mappings that reference guidance from ENISA as well as documentation published by the Australian Cyber Security Centre, which helps startups operating across borders maintain a unified control set. The platform’s transparency features allow external auditors to review the underlying logic without proprietary restrictions, and this openness has encouraged wider adoption among venture-backed companies seeking to avoid vendor lock-in. Figures from recent industry analyses reveal that open compliance platforms correlate with higher completion rates for first-time audits when compared with closed-source alternatives.
Technical Architecture and Extensibility
The system relies on containerized components that deploy alongside existing CI/CD pipelines, and contributors have added support for additional cloud providers through pull requests that undergo peer review. Because the project remains fully open source, organizations can audit the scanning algorithms themselves rather than relying solely on vendor assurances. Data indicates that this level of visibility shortens the trust-building phase with enterprise prospects who demand proof of security posture before signing contracts.
Future Developments and Broader Implications
Upcoming releases scheduled after October 2026 plan to incorporate machine-learning models that predict potential control failures based on historical scan data, which could further compress audit timelines. Collaboration with research institutions continues to refine these predictive elements while preserving the open nature of the codebase. Observers expect continued growth in usage as more startups recognize that compliance can become an operational advantage rather than a recurring bottleneck when supported by extensible tooling.
Conclusion
KnoxOpen has altered the compliance landscape by embedding audit readiness into daily development workflows, and the measurable reductions in preparation time documented across multiple sectors demonstrate its practical value. As regulatory requirements evolve, the platform’s open architecture positions it to adapt alongside new standards without requiring complete reimplementation by each adopting organization. Those tracking security tooling trends note that such shifts toward integrated, transparent solutions reflect broader movement within the startup ecosystem toward sustainable security practices.