Noah Vogel · 13 September 2026
Navigating Integration Challenges with Advanced Open Security Platforms in Corporate Settings
Understanding Open Security Platforms in Modern Enterprises
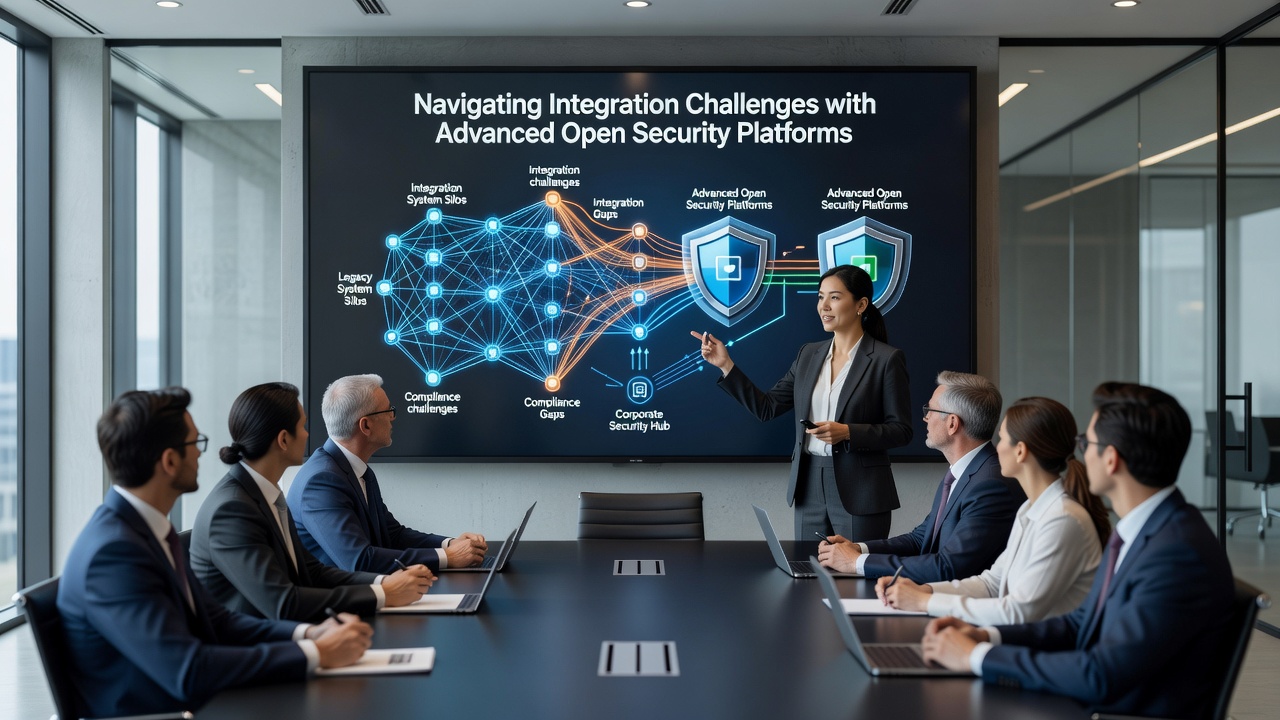
Advanced open security platforms rely on open standards and often open-source components to deliver threat detection, access control, and data protection across distributed corporate networks, and organizations adopt them to reduce vendor lock-in while meeting evolving compliance demands. These platforms integrate with existing infrastructure such as cloud environments, on-premises servers, and endpoint devices, yet compatibility gaps frequently surface during deployment because legacy systems use proprietary protocols that conflict with open APIs. Data shows that enterprises encounter delays when mapping these protocols, and the resulting configuration mismatches require extensive testing cycles before full functionality emerges.
Key Integration Barriers Across Corporate Environments
One primary obstacle involves identity and access management alignment, since many corporations maintain hybrid identity stores that combine on-site directories with cloud-based services, and open security platforms demand precise synchronization to avoid authentication failures. Another barrier arises from network segmentation requirements, where traffic inspection rules must accommodate both high-volume data flows and strict latency thresholds, while mismatched encryption standards create bottlenecks. Observers note that scalability testing often reveals performance drops when platforms scale to thousands of endpoints simultaneously, and this forces teams to recalibrate resource allocation mid-project. Regulatory timelines add pressure, particularly as new reporting mandates take effect in September 2026 under updated cross-border data protection frameworks that require auditable logs from all security layers.
Technical Compatibility and Data Flow Considerations
Engineers must map data schemas between open platforms and proprietary monitoring tools, and this mapping process exposes inconsistencies in event formatting that disrupt centralized analytics dashboards. Studies from research institutions indicate that up to 40 percent of integration time goes toward custom middleware development when native connectors fall short, and such development introduces maintenance overhead that persists long after initial rollout. Network address translation conflicts further complicate matters in multi-site deployments, whereas consistent use of standardized protocols like TLS 1.3 and JSON-based logging reduces these friction points. Those who've managed large-scale projects often discover that early proof-of-concept environments fail to replicate production traffic patterns, leading to late-stage surprises that extend timelines by weeks or months.
Organizational and Process-Related Hurdles
Cross-team coordination presents its own set of difficulties because security operations, infrastructure, and application development groups maintain separate priorities and change-management procedures. When an open platform update alters API behavior, downstream applications may break unless version control processes include all stakeholders from the outset. Training requirements also grow because staff accustomed to closed ecosystems need time to master open configuration languages and community-supported troubleshooting methods. Figures from industry reports reveal that organizations investing in structured knowledge transfer programs complete integrations 25 percent faster than those relying on ad-hoc learning, and this gap widens when multiple geographic regions participate in the rollout.
Approaches That Improve Deployment Outcomes
Phased rollouts allow teams to validate each module before expanding scope, and this method limits the blast radius of any configuration error. Automated testing frameworks that simulate realistic attack traffic help confirm that new controls do not degrade business-critical applications. Partnerships with academic research groups have produced reference architectures that document successful patterns for combining open security components with enterprise resource planning systems, and several corporations reference these architectures when updating their internal playbooks. According to the NIST Cybersecurity Framework, continuous monitoring combined with documented rollback procedures forms a baseline for managing integration risk across evolving technology stacks.
Looking Ahead to September 2026 and Beyond
Anticipated updates to international cybersecurity directives scheduled for September 2026 emphasize machine-readable incident reporting that open platforms must support natively, and early adopters already prototype the necessary export modules. The European Union Agency for Cybersecurity has published guidance on modular security architectures that aligns with these forthcoming requirements, providing templates for logging and alerting that reduce custom development work. Companies tracking these developments allocate budget for incremental upgrades rather than wholesale replacements, since open platforms permit targeted component swaps without disrupting the entire stack.
Conclusion
Successful navigation of integration challenges depends on thorough compatibility assessments, coordinated cross-functional processes, and alignment with emerging regulatory schedules such as those arriving in September 2026. Organizations that treat open security platforms as evolving ecosystems rather than static products maintain flexibility while satisfying both operational and compliance objectives. Data from multiple sectors continues to show that methodical planning combined with standardized interfaces yields measurable reductions in deployment friction over successive projects.